Turn Abnormal Activity Into Actionable Security Context
Every network generates thousands of signals a day, and most are noise. Ennetix xVisor’s Threat Insights capability helps IT and security teams surface abnormal activity in context so they can focus on what actually requires investigation.
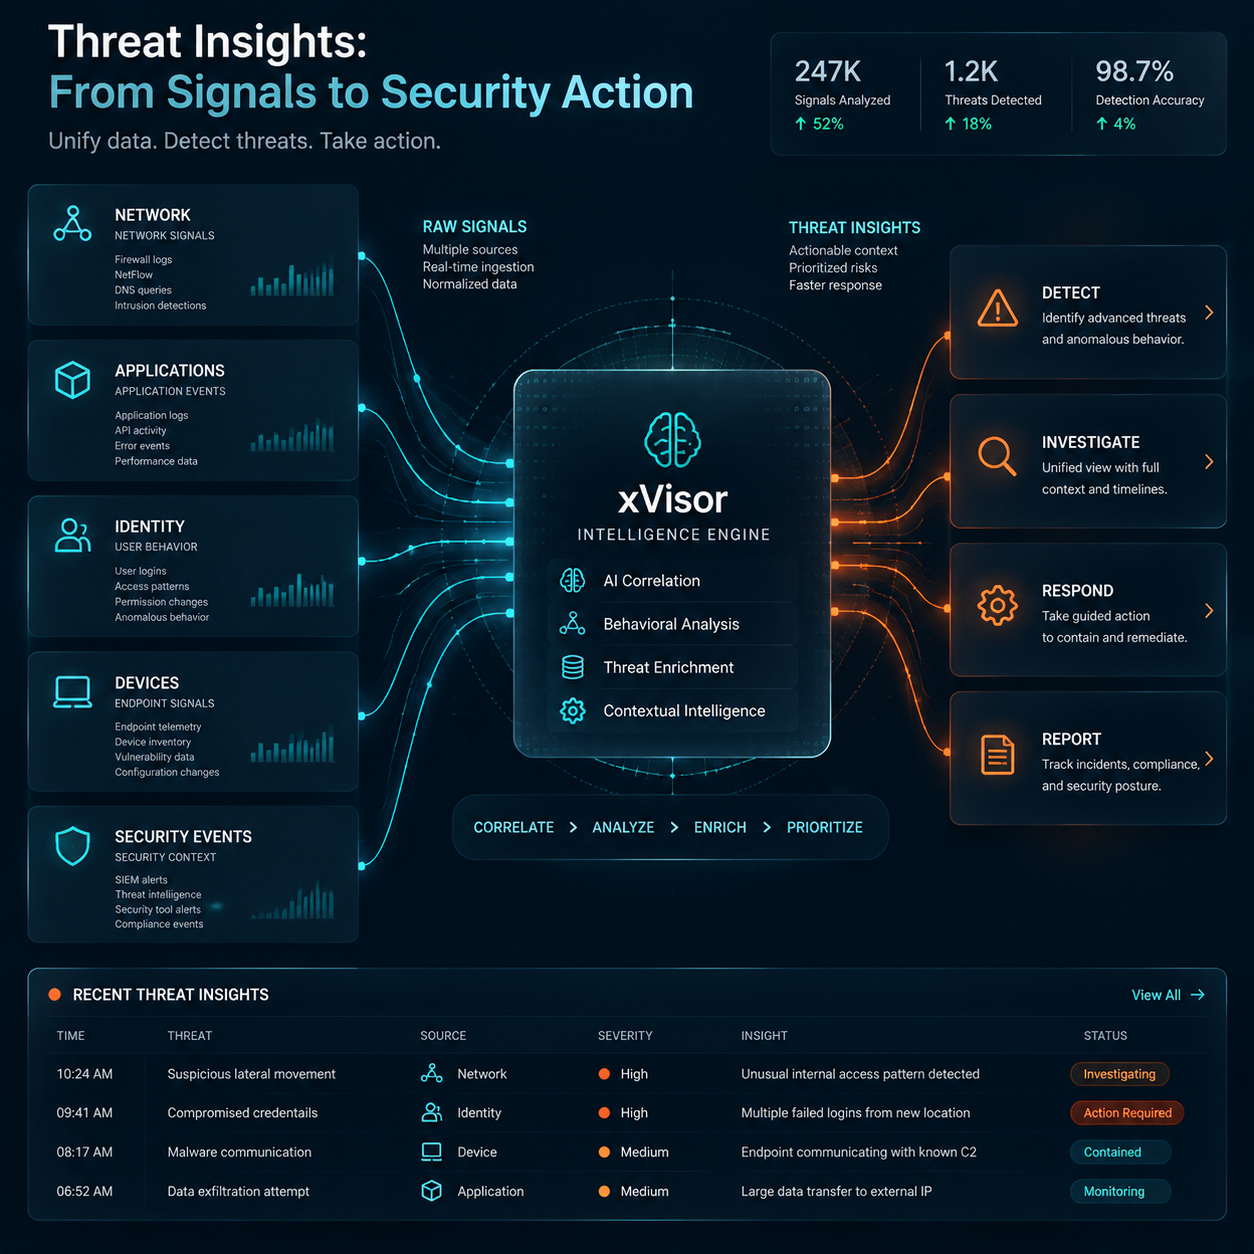
xVisor turns fragmented network, application, and infrastructure signals into contextual threat insights. Built on xVisor’s network and application provenance data, it helps teams understand unusual activity, affected systems, and related behavior without treating every anomaly as a confirmed threat.
An anomaly is a starting point for investigation, not proof of malicious activity. xVisor provides the operational context teams need to investigate and make that determination.
The Challenge
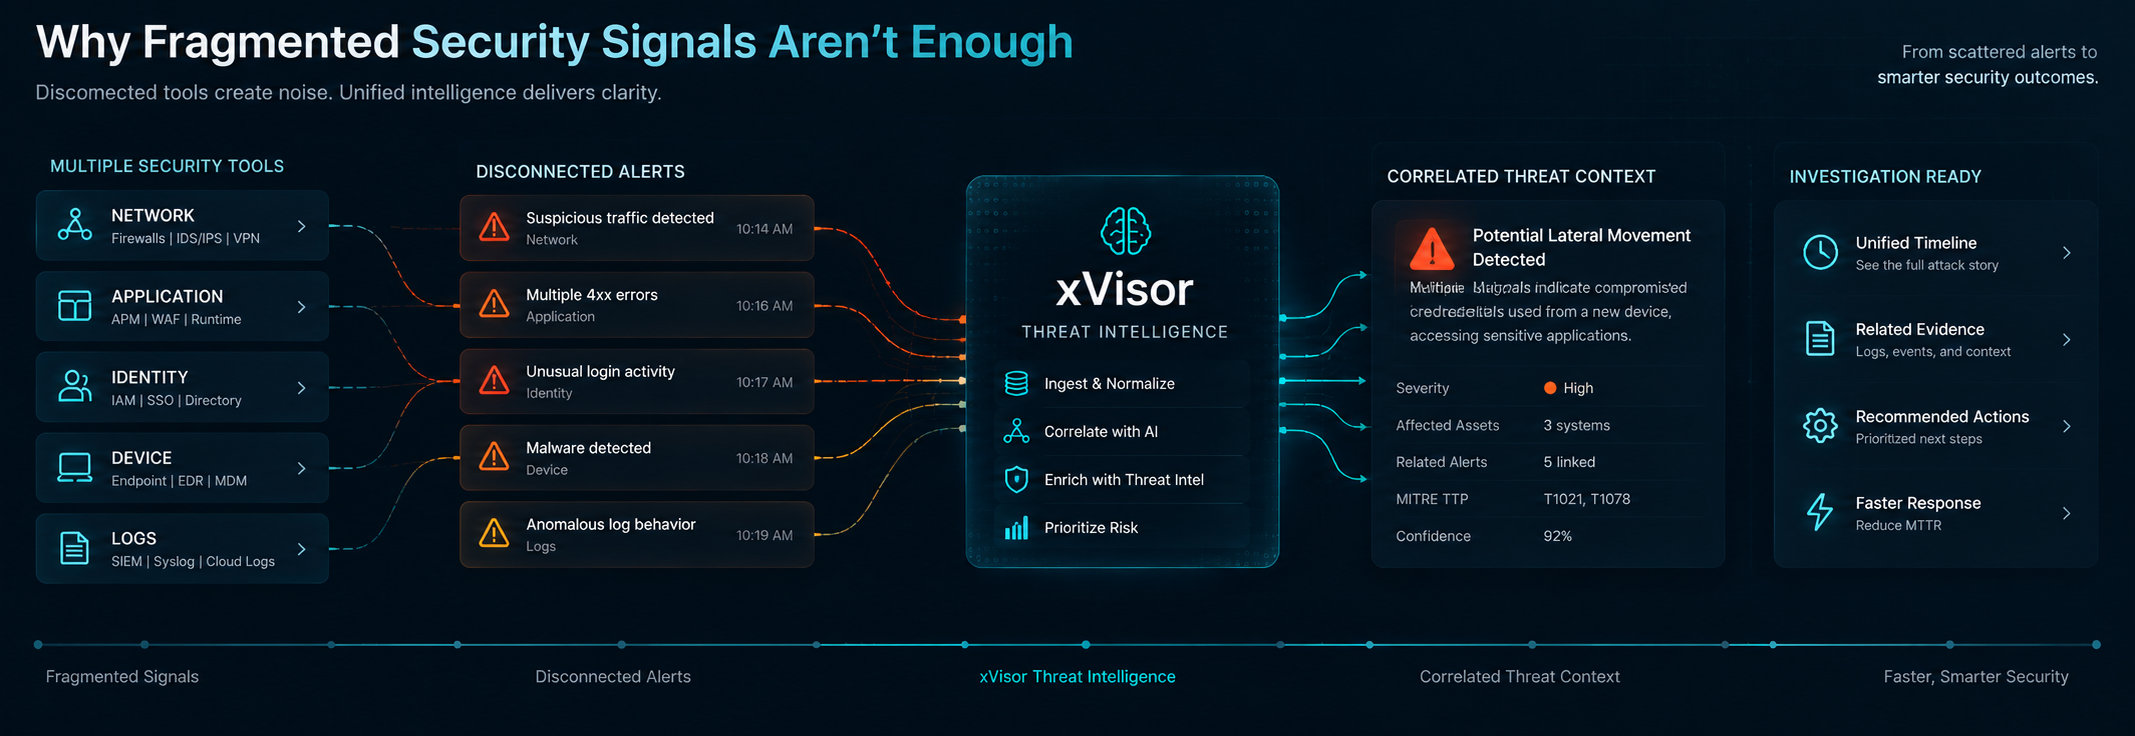
Why Fragmented Security Signals Aren’t Enough
Security and operational data often live in separate systems, with network telemetry in one tool, application performance in another, and identity events elsewhere.
This fragmentation makes early-stage threats difficult to investigate because teams must manually determine:
xVisor brings these signals together so teams can move from isolated alerts to contextual security insight.
The xVisor Approach
How xVisor Delivers Threat Insights
Detect Abnormal Activity
xVisor continuously monitors network and application behavior to identify deviations such as unusual traffic patterns, unexpected authentication behavior, and performance changes with possible security relevance.
See Threats in Operational Context
Connect network, application, infrastructure, device, user, and authentication relationships so that abnormal events can be investigated with the surrounding context.
Strengthen Security Observability
The same telemetry used for observability and root-cause analysis also supports security-relevant detection. Continuous User and Entity Behavior Analytics (UEBA) adds behavioral context across user and application relationships.
Support Zero-Trust Visibility
xVisor establishes device, application, user, and authentication provenance to support continuous visibility and verification. It complements Zero-Trust controls but does not replace access control, policy engines, or identity platforms.
Investigate With Historical Context
Retained network and application telemetry helps teams understand when abnormal behavior started, what changed beforehand, and which systems experienced related activity.
Connect Situational Awareness With Threat Insights
Situational Awareness shows what is happening across the environment. Threat Insights help identify which activity may carry security significance and deserves closer investigation.
Data and Integration Support
Depending on deployment, xVisor can draw on network packet and flow telemetry, application and host activity, identity and authentication data, and existing IT or security workflows.
Impact
Business Outcomes
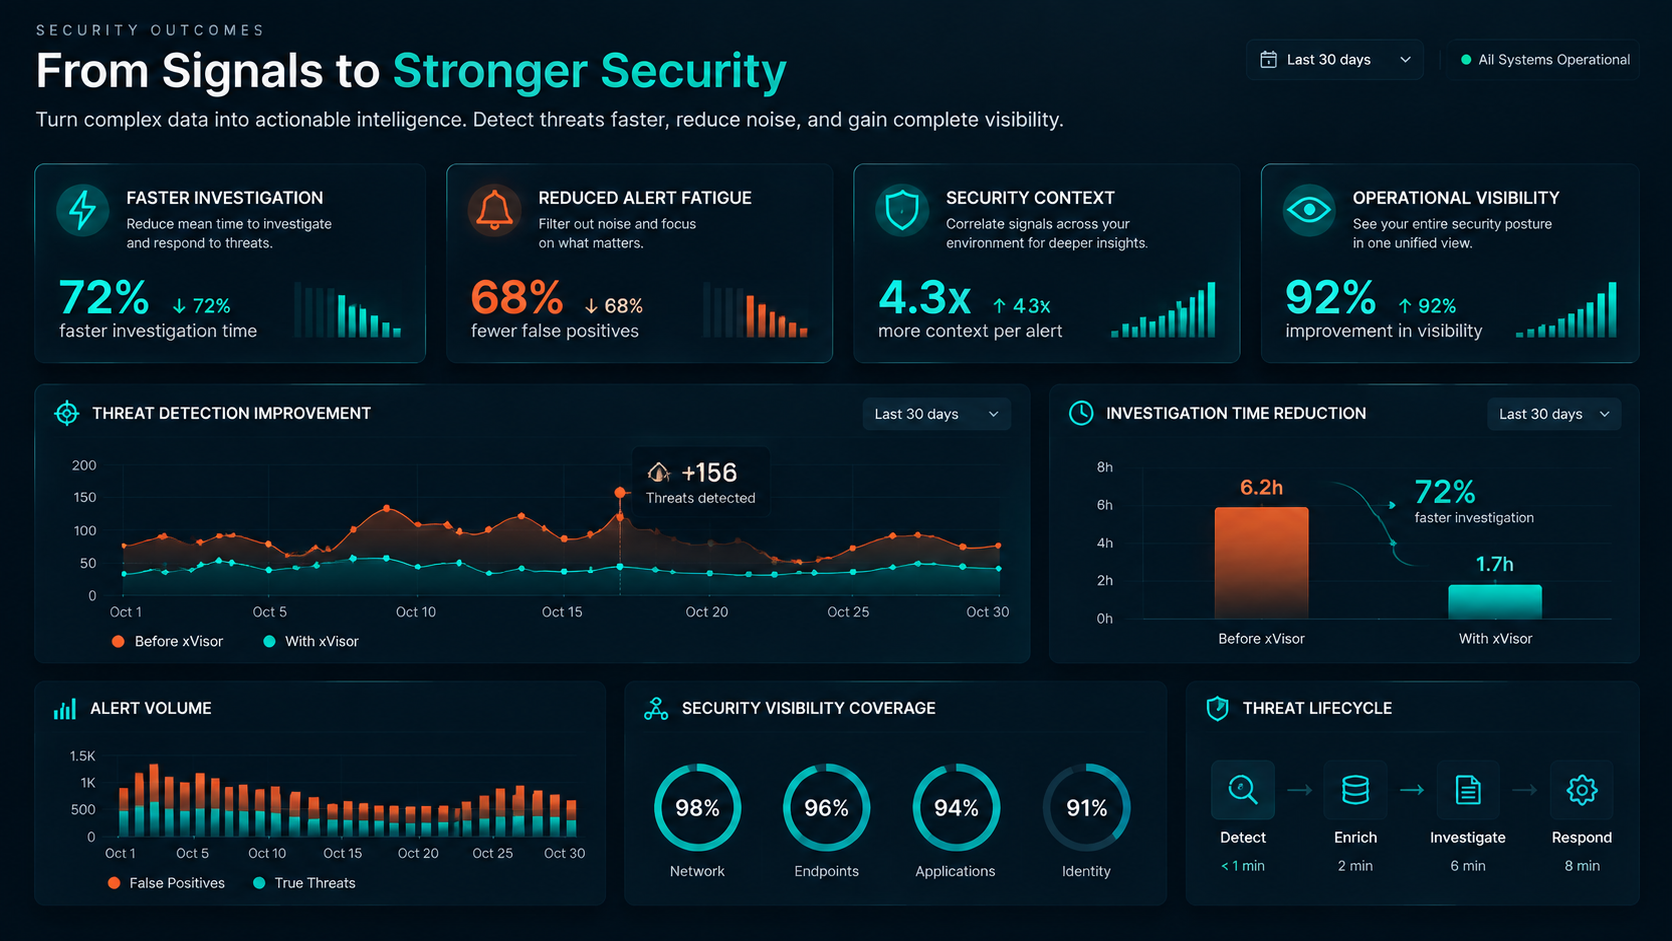
xVisor helps security and IT teams reduce the manual effort required to identify, correlate, and investigate abnormal activity across complex environments.
By connecting behavioral analytics with operational telemetry, xVisor helps teams move from raw signals to prioritized investigation without replacing the security tools already in place.
A Threat-Insights solution helps IT and security teams turn raw network, application, and behavioral signals into contextual information that can be prioritized and investigated.
No. xVisor identifies activity that deviates from established behavior. Determining whether that activity is malicious requires further investigation using the context provided.
xVisor provides continuous visibility into device, user, application, and authentication activity, helping teams make existing Zero-Trust controls more informed. It does not replace identity, access-control, or policy-enforcement platforms.